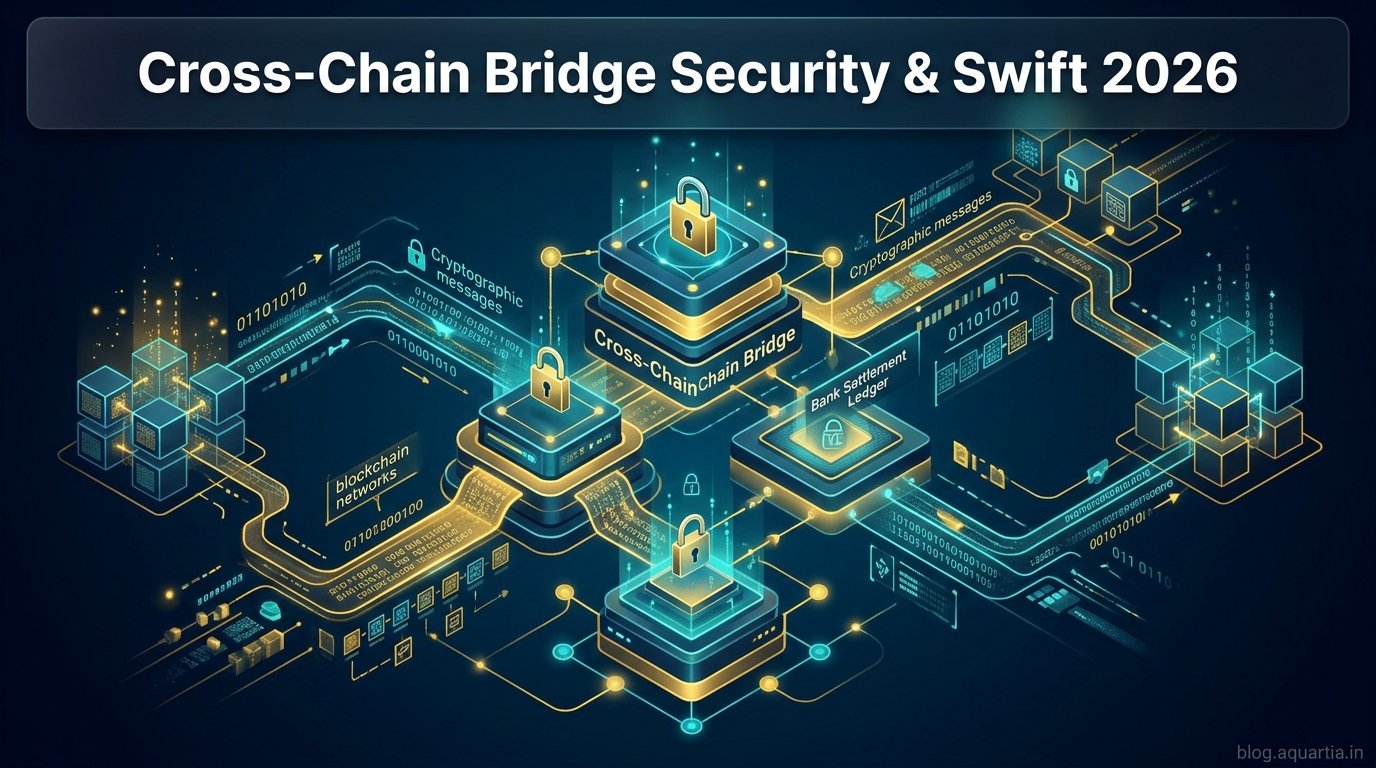
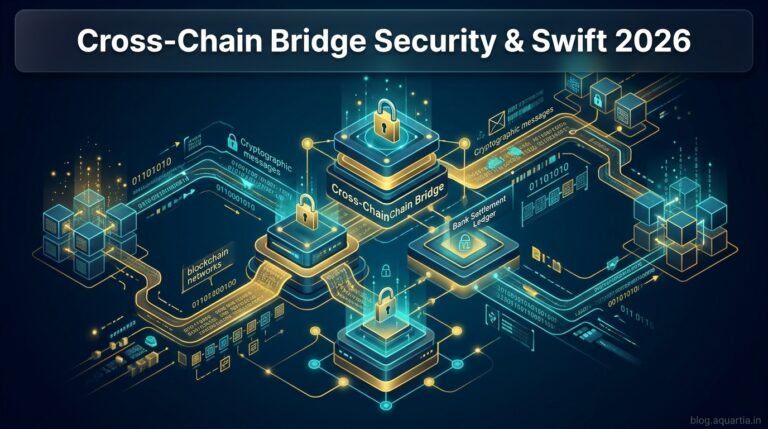
Liquidity in 2026 is fragmented across Layer 1s, rollups, appchains, and private enterprise ledgers—making blockchain interoperability essential, yet bridges remain crypto’s most targeted attack surface (PixelPlex).
The Core Security Lesson: Who Verifies the Message?
In April 2026, a single forged cross-chain message drained roughly $292 million from Kelp DAO’s LayerZero-based bridge, echoing earlier multisig and verifier failures such as Ronin and Nomad (PixelPlex). Safe interoperability designs in 2026 increasingly favor:
1. Native Burn-and-Mint (e.g., Circle CCTP) and Light Clients (e.g., IBC): Eliminate pooled collateral honeypots that lock-and-mint bridges create (PixelPlex).
2. Hardened Verifier Quorums: Avoid single-verifier configurations in protocols like LayerZero, Hyperlane, or Chainlink CCIP 2.0.
3. Institutional Cross-Chain Rails: In July 2026, Swift declared its blockchain ledger ready for initial use with 17 banks preparing pilots (PixelPlex).
Internal & Further Reading
Read our Interoperable Blockchain Networks overview.
Frequently Asked Questions
Why are cross-chain bridges so frequently hacked?
Most major bridge exploits stem from compromised validator keys, weak signer thresholds, or flawed message-verification logic rather than bugs in the underlying L1 chains (PixelPlex).

+ There are no comments
Add yours